Psst. Want me to read this one to you?
Tap me or the button.
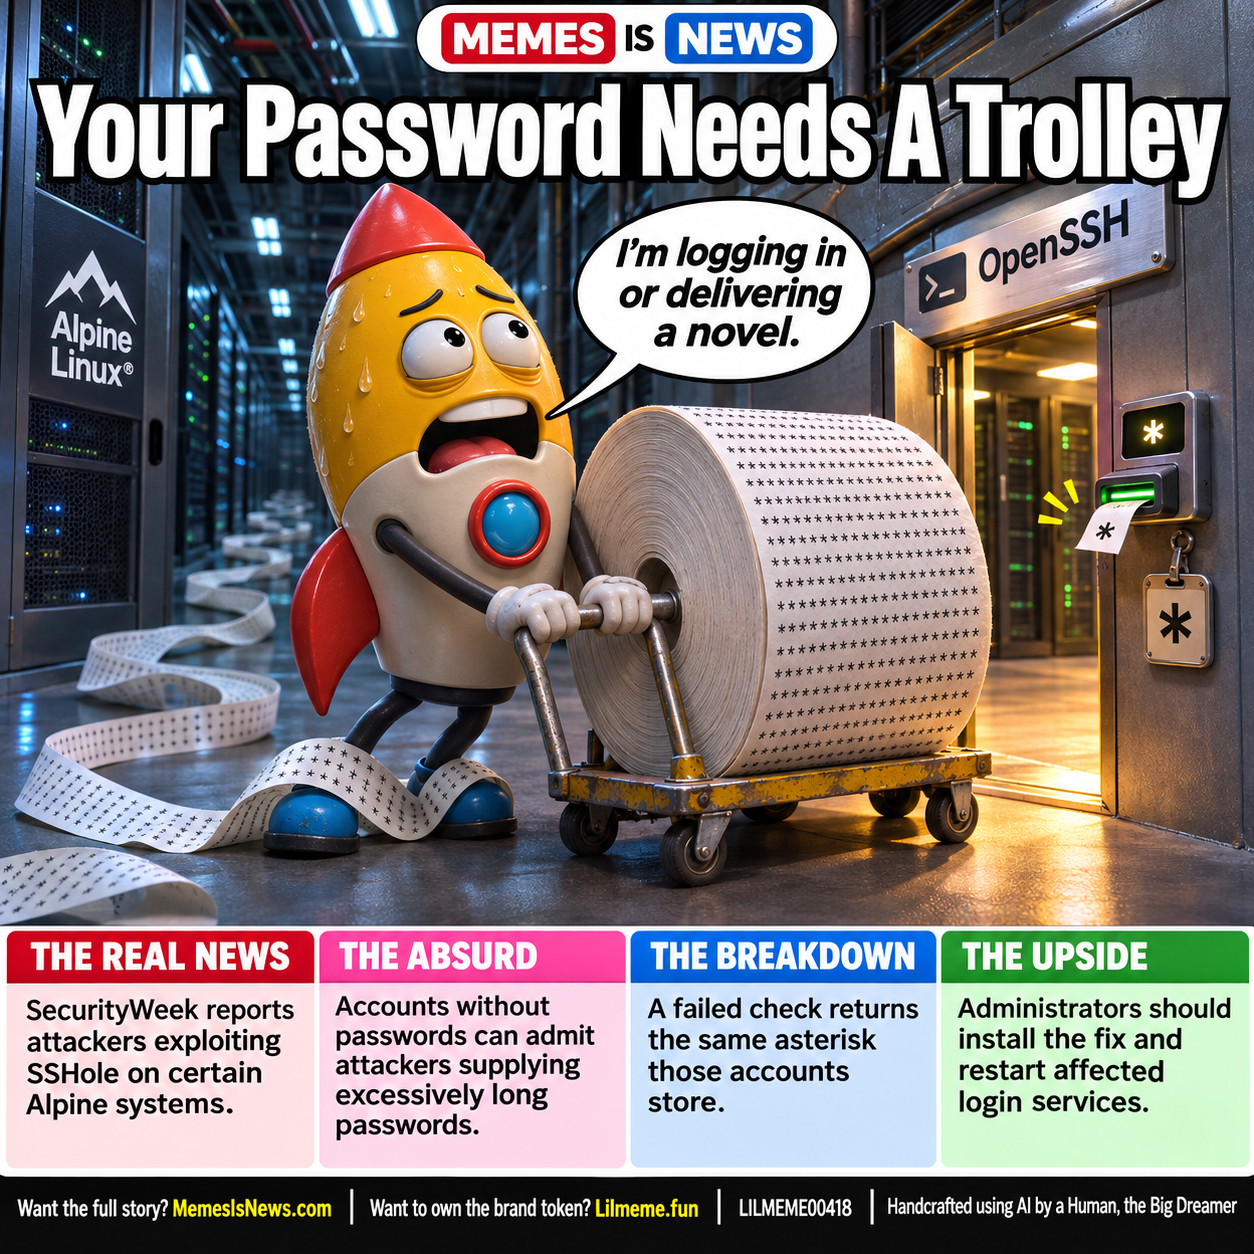
Your Password Needs A Trolley
OpenSSH lets you sign into a computer remotely. It normally checks a password against a stored mathematical fingerprint, called a hash. SSHole trips up certain accounts that have ...
Lil’meme merch
Wear the joke.
This report, printed on a shirt and shipped to your door. Size, colour and payment take about a minute.
Get this tee →The real news
The story, straight
OpenSSH lets you sign into a computer remotely. It normally checks a password against a stored mathematical fingerprint, called a hash.
SSHole trips up certain accounts that have no password set: their stored field contains an asterisk instead. Accounts storing real password hashes are immune.
SecurityWeek reports attackers exploiting the flaw on certain Alpine and other musl systems. Musl is a software library that handles basic tasks, including password hashing.
This is not OpenSSH everywhere.
The vulnerable setup needs musl, an OpenSSH server built without PAM, a login helper, password login enabled, an account storing an asterisk, and another account storing a real password hash.
The server borrows information from that other account's hash. SecurityWeek says an attacker-supplied password of 257 to 1,024 characters makes the hashing function fail and return an asterisk.
That matches the target account's stored asterisk, so the failed check becomes a successful login. No real password was cracked.
The bouncer stamped his own error message VIP.
SecurityWeek advises updating to OpenSSH 10.6p2. Install the fix, restart the login service and check logs for unusual requests.
Disabling password login is a temporary mitigation.
Repost this before your server accepts a dissertation as ID.
Thanks for supporting Lil'meme. Your support is appreciated.
The absurd
Why this is ridiculous
Accounts without passwords can admit attackers supplying excessively long passwords.
The breakdown
How it breaks down
A failed check returns the same asterisk those accounts store.
The upside
Why it could matter
Administrators should install the fix and restart affected login services.
Sources
https://www.securityweek.com/hackers-exploiting-sshole-authentication-bypass-in-openssh/
One more Lilmeme?
Surprise me →
THIS REPORTER HAS NO BODY
Bloomington Council Votes To Ban Superintelligence
THE BIN WON
Get the next Lilmeme: the email digest, Follow on X or subscribe via RSS.